Deploying Microsoft 365 Copilot is not simply a matter of purchasing licences and enabling a feature. Copilot uses the information each user can already access in Microsoft 365. When permissions are consistent, its responses can be useful and controlled. When content is shared too broadly, the tool can make that exposure easier to exploit.
For an SME, the right starting point is therefore data and access governance. You need to know which workspaces exist, who owns them, which people or groups can view their content, which links remain active, and which sensitive information requires stronger protection.
The approach below follows five simple movements: discover, correct, govern, pilot, and measure. It aims for proportionate preparation without blocking legitimate work or turning the project into an endless audit.
In this article
- Understand what Copilot changes about information access
- Map SharePoint, OneDrive, and collaboration workspaces
- Step 1 — Detect excessive access and oversharing
- Step 2 — Correct priority gaps without blocking teams
- Step 3 — Govern workspaces, owners, and their lifecycle
- Protect sensitive data with proportionate controls
- Run a representative pilot before general deployment
- Measure results and address access drift
- Checklist before enabling Microsoft 365 Copilot
Understand what Copilot changes about information access
Copilot can search, summarise, and connect information from Microsoft 365 in the user’s context. It does not automatically create new SharePoint permissions: it respects the access, sharing settings, and policies already in place.
The main risk therefore comes from pre-existing exposure. A forgotten document on a site available to an overly broad group may previously have been difficult to find. Assisted search can make its content visible and usable much more quickly by people who are already authorised.
This distinction prevents two mistakes: treating Copilot as inherently dangerous, or assuming it is safe to enable simply because permissions already exist. The project must verify that those permissions still match current roles and needs.
Preparation must preserve legitimate work. The goal is not to close every access path, but to reduce oversharing, clarify responsibilities, and ensure that useful content remains available to the right people.
Map SharePoint, OneDrive, and collaboration workspaces
Begin by inventorying SharePoint sites, connected Teams workspaces, relevant OneDrive libraries, and other collaboration spaces used by the target population. Record their activity, sensitivity, owners, and business purpose.
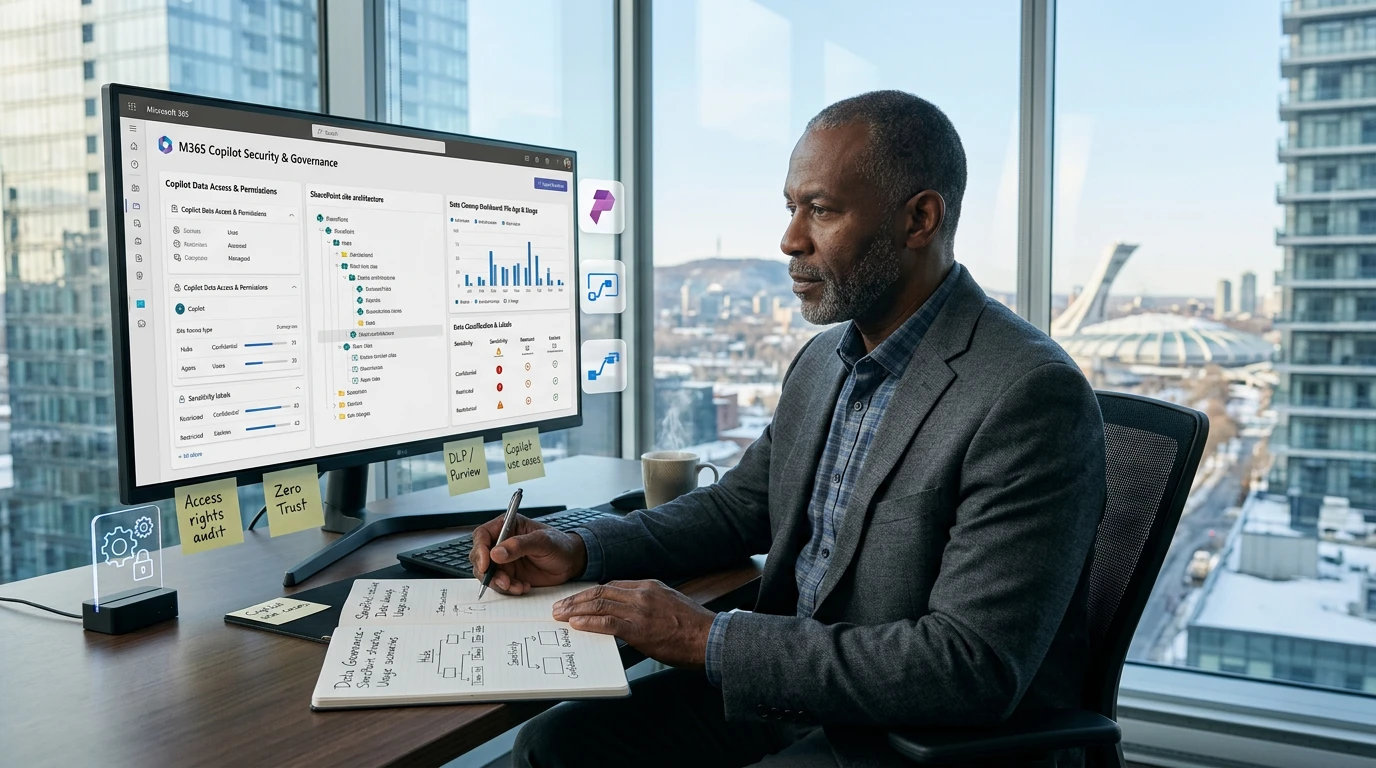
Identify sites without an active owner, abandoned workspaces, very broad groups, external guests, and open sharing links. SharePoint data access governance reports can help identify sites with potential oversharing or sensitive content.
Do not stop at a technical list. Associate each workspace with someone who can explain why it exists, who should have access, and how long its content should be retained. Without a business owner, an anomaly is difficult to resolve.
Then rank workspaces by priority: sensitive data, broad audience, high activity, missing ownership, or uncertain use. This map helps focus effort where remediation will create the most value.
Step 1 — Detect excessive access and oversharing
The discovery phase looks for concrete gaps: members who no longer have a role, guests who have never been reviewed, groups containing too many people, “anyone with the link” sharing, broken permission inheritance, and sensitive files exposed too broadly.
Review inactive workspaces as well. An abandoned site may still contain important documents while falling outside routine management. A lack of activity does not make its exposure harmless.
Document each finding with the affected site, type of access, exposed population, expected owner, and required decision. Avoid deleting immediately: first confirm the actual use with the business owner.
For an SME, a simple tracking table is often enough. The essential task is to distinguish critical risks from desirable improvements and assign every action clearly.
Step 2 — Correct priority gaps without blocking teams
Correct first the exposures that combine sensitive content with an overly broad audience. Remove obsolete accounts, tighten groups, review guests, and replace open links with links limited to approved people or groups.
Work in controlled batches. A mass correction can interrupt a legitimate process or prevent a team from reaching its documents. Test business workflows after each set of changes and preserve the ability to reverse a decision.
High-risk sites may require temporary measures during analysis. These restrictions should remain proportionate, documented, and removed once permissions have been properly remediated.
Every exception should have a reason, an owner, and a review date. A permanent exception without ownership quickly becomes another source of drift.
Step 3 — Govern workspaces, owners, and their lifecycle
A one-time correction is not enough. Define who may create a site, invite an external person, generate a sharing link, and approve an exception. The rules should be understandable and appropriate to the organisation’s size.
Every workspace should retain at least one active owner, ideally two to avoid dependence on one person. Their responsibilities cover members, guests, content, classification, and periodic access reviews.
Plan a lifecycle: creation, use, review, archiving, and deletion. Inactive workspaces should be reported to their owner, then archived or deleted according to operational needs and retention obligations.
Use naming conventions and creation templates to make workspaces easier to understand. Visible governance reduces mistakes and makes future reviews easier.
Protect sensitive data with proportionate controls
Identify the information categories that require stronger protection: personal data, contracts, financial information, HR records, trade secrets, or documents subject to regulatory obligations.
Sensitivity labels, data loss prevention policies, and access controls can complement SharePoint permissions. Their configuration should follow the actual classification of information and the licences available.
Avoid applying the maximum restriction everywhere. Excessive controls encourage teams to work around the tools. Start with high-impact scenarios and verify that users understand the rules.
Protection must also cover content quality. Duplicates, outdated documents, and conflicting versions reduce the relevance of responses. Good information hygiene improves both security and usefulness.
Run a representative pilot before general deployment
Before a general deployment, choose a pilot population representing several functions, sensitivity levels, and working habits. A pilot limited to the IT team will not reveal the everyday difficulties experienced by business users.
Define precise scenarios: finding a procedure, summarising a case file, preparing a meeting, or comparing several documents. For each scenario, record the expected result, information that must not appear, and acceptance criteria.
Prepare support before assigning licences. Users must know where to ask a question, report an unexpected result, and request a correction to access or content.
Collect feedback on relevance, time saved, errors, training needs, and incidents. Use these findings to correct the environment before expanding the deployment.
Measure results and address access drift
After activation, monitor usage and drift. Teams change, guests accumulate, new sites appear, and sharing links multiply. An environment that is clean at launch can deteriorate quickly.
Track a few actionable indicators: sites without owners, guests not reviewed, open links, inactive workspaces, overdue corrective actions, reported incidents, and resolution rates.
Hold a regular review involving IT, security, and business owners. Reports should lead to assigned decisions with deadlines, not an accumulation of observations.
Measure value as well: scenarios actually used, time saved, perceived quality, and sustained adoption. Governance helps maintain trust as much as it protects data.
Checklist before enabling Microsoft 365 Copilot
Before enabling Microsoft 365 Copilot, verify the following:
- the relevant SharePoint, OneDrive, and Teams workspaces have been inventoried;
- every site has an identified owner;
- guests have been reviewed;
- open or overly broad sharing links have been checked;
- priority excessive access has been corrected;
- sensitive data has been identified and protected;
- creation, sharing, and lifecycle rules have been defined;
- a representative pilot population has been chosen;
- a support process is in place;
- indicators and review frequency have been defined.
This checklist does not replace analysis of your context. It provides a minimum threshold for deciding whether the organisation can begin a controlled pilot or whether certain risks must first be addressed.
Keep the evidence: dated inventories, decisions, exceptions, test results, and corrective actions. These records make follow-up easier and prevent the analysis from starting over at each stage.
Key takeaway: Copilot does not replace governance. Reliable adoption depends on justified access, controlled content, identified owners, and continuous improvement.
Sources and references
“Copilot does not replace access governance: it makes the quality of existing permissions and information more visible.”
ALLFORWEB Method
Let’s grow together
Is your Microsoft 365 environment ready for Copilot?
Let us assess your SharePoint access, oversharing risks, and priority controls before launching a Copilot pilot.